
One-minute news
▶ Refrigeration and freezer systems at hundreds of French supermarkets were heated in a cyberattack overnight on Oct. 11, forcing the disposal of large quantities of fresh and frozen food. Prosecutors are investigating whether fires at some stores were linked to the attack.
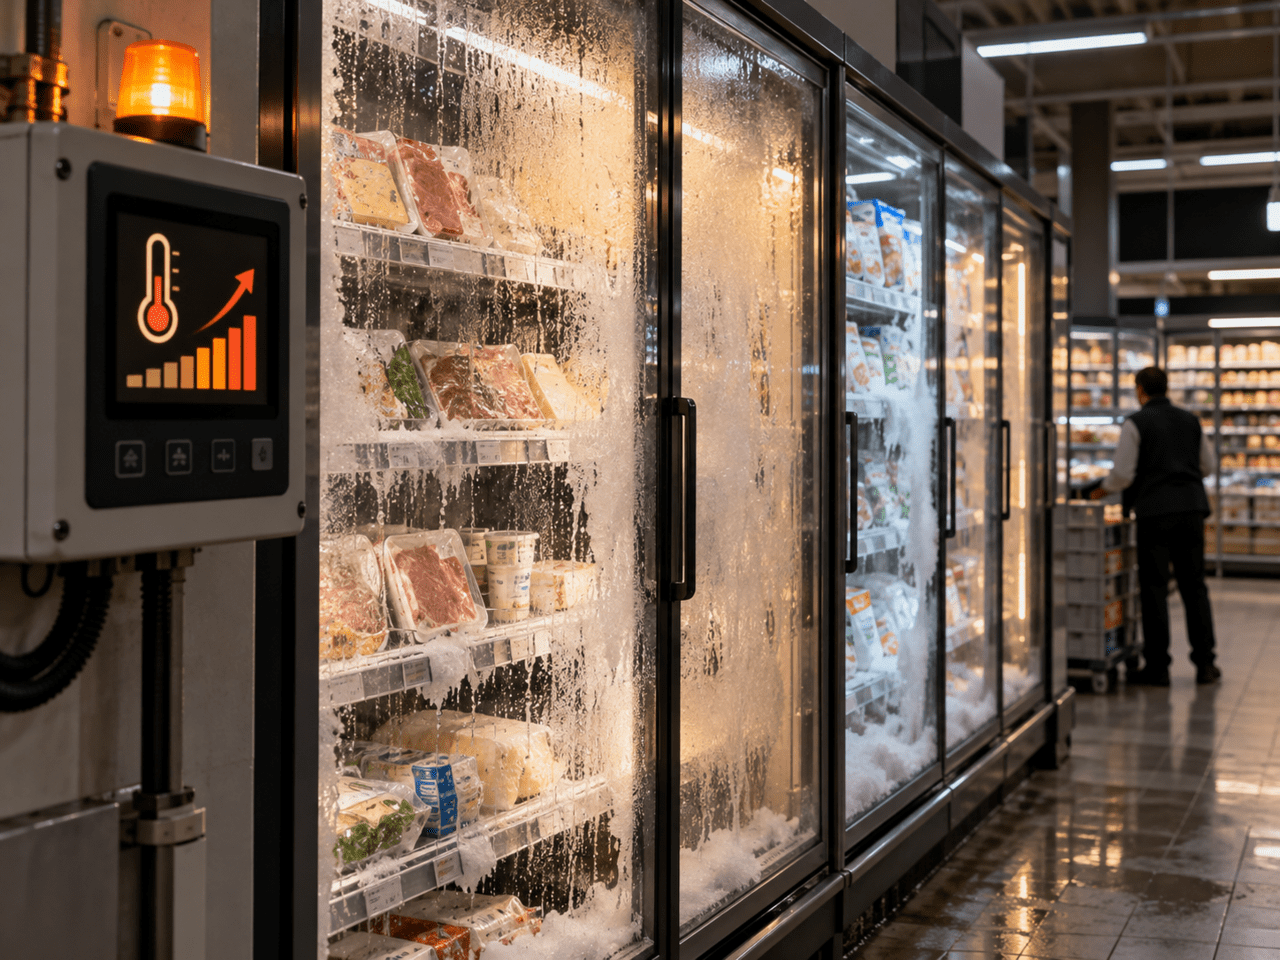
▶ The hackers did not steal data or lock up computer networks. Instead, they remotely activated the refrigeration systems’ defrost function, raising temperatures to as high as 50 degrees Celsius.
▶ The affected systems were reportedly older Danfoss products or devices that had not been updated. Similar systems were targeted in Russia and Israel in 2022.
What happened
Refrigeration and freezer systems operated by major French retailers were hit by a series of cyberattacks. According to AFP, the attacks took place between the night of Oct. 11 and the early hours of Oct. 12 local time.
At least 300 Intermarché and Netto stores, a related brand, and more than 100 Coopérative U stores were affected. Carrefour confirmed damage at 80 locations, while E.Leclerc and Monoprix were also impacted. Le Monde reported on Oct. 13 that the effects had spread to wholesaler Metro and meat-processing companies.
The hackers remotely activated the refrigeration systems’ defrost function, which melts frost that builds up inside the equipment. According to Le Monde, the defrost temperature rose to 50 degrees Celsius and the operating time was extended from one hour to as long as eight hours. Les Mousquetaires, the operator of Intermarché, said the equipment was heated to as high as 50 degrees for about six hours. The affected stores discarded all of their fresh and frozen food.
The Paris prosecutor’s office assigned the investigation to the Office for the Fight Against Cybercrime (OFAC). Investigators are examining which businesses were affected, the resulting food losses, and whether reports of fires were connected to the attacks. Prosecutors confirmed that fires occurred at some stores, but their cause has not been determined. No group has claimed responsibility. The final number of affected stores has yet to be established, as estimates vary depending on when they were compiled.
Why it matters
No personal data breaches or computer network outages have been reported in the attack. French IT outlet InformatiqueNews said the attackers used the equipment’s normal automatic defrost function rather than encrypting data or shutting down business systems.
The damage included discarded food, equipment damage and fires. The incident is seen as an example of a cyberattack whose effects extended beyond computer systems to inventory and on-site safety.
Danfoss refrigeration system controllers have been identified as a common factor. The controllers centrally manage temperature settings, operating schedules and alerts for multiple refrigeration units in a store. They also provide a web-based interface that maintenance contractors can use for remote inspections.
According to an investigation by cybersecurity company SOKRADER on Oct. 13 local time, 4,481 of these management interfaces were discoverable online worldwide, about 65% of them in France.
Aging equipment is also considered a contributing factor. Danfoss told Reuters that the affected systems were running outdated firmware, the basic software embedded in a device. Support for some older models ended in 2016 and 2021, leaving them without security updates.
Similar systems have been attacked before. Danfoss technical documents say 16 Russian supermarkets and 40 stores in Israel were targeted in 2022. The Israeli stores did not have firewall or virtual private network (VPN) protection in place.
In August, cybersecurity company Claroty disclosed a vulnerability in the latest model of the device that could allow administrators’ authentication to be bypassed. At the time, it also identified 2,765 devices accessible from the internet.
Different views
Views differ over who is responsible. Danfoss says it has long advised customers to update their systems and replace older equipment.
Researcher Tellier said the issue appears to lie with store operators and the refrigeration contractors who install and manage the systems. He described the management interface’s exposure to the internet and weak authentication as “a double mistake.” However, several authentication-bypass vulnerabilities in the device have been reported since 2023.
The method of entry has not been confirmed. French authorities and Danfoss have not disclosed which vulnerability was used in the attack. SOKRADER said the attackers may have directly breached devices exposed to the internet, or compromised remote-management channels used by maintenance contractors. Tellier said it could not be concluded that a vulnerability previously discovered by Synacktiv was used in this attack.
What it means
The financial losses have not been calculated. Les Mousquetaires CEO Thierry Cotillard was reportedly cited as estimating the total damage in France at tens of millions of euros. Costs are expected to include not only discarded food but also equipment replacement, restocking and business interruptions.
The French government has taken action at the national level. Prime Minister Sébastien Lecornu assigned the case to the National Cybersecurity Agency of France (ANSSI). On Oct. 12, the national incident response team CERT-FR issued an alert, advising operators to disconnect the devices from the internet or strictly restrict access to them.
Some say the scope of operational technology (OT) security—which has traditionally focused on factories and power plants—needs to be expanded.
Solutions
At a briefing on Sept. 21, the Korea Internet & Security Agency (KISA) said the number of publicly disclosed security vulnerabilities worldwide rose from 29,066 in 2023 to 48,185 last year, and is projected to reach 66,000 this year.
The spread of AI tools that can independently find vulnerabilities is seen as a major factor behind the increase. Twenty-nine percent of vulnerabilities were exploited on or before the day they were publicly disclosed. Meanwhile, the average time companies take to fix vulnerabilities has lengthened from 32 days to 43 days.
The gap is even wider for equipment. Servers can be updated remotely, but refrigeration and air-conditioning systems often require a technician to visit the site. For older devices that are no longer supported, updates may not be available at all.
Emergency measures taken by French authorities point to a possible response. CERT-FR advised operators to disconnect equipment management devices from the internet. SOKRADER recommended installing temperature alarms that operate independently of the controllers. These are considered effective precautions in an environment where hundreds of new vulnerabilities emerge every day.
Japan offers a relevant example. In 2022, ransomware infection at one supplier shut down 14 Toyota plants. Since then, Japanese automakers have tied supplier security checklists to business evaluations and established systems in which large companies help their suppliers improve security.
Efforts to use AI for defense are also beginning. In September, South Korea’s Ministry of Science and ICT selected a Naver Cloud-led consortium to develop an independent AI model specializing in cybersecurity.
At an event on Oct. 7, Lee Jong-hyuk, director of the ministry’s Information Security Industry Division, said the project was launched because reliance on foreign AI models could limit how they are used.
KISA has established a vulnerability management center and put in place a system to quickly distribute vulnerability and security patch information to chief information security officers (CISOs) and others at about 28,000 companies.